
The problem with vulnerabilities is rarely finding them. Scanners report the same issue more than once, ownership is unclear, and it’s hard to tell what’s actually exploitable. So teams end up fixing what scores highest, not what matters most.
With Tines 3B, you decide how findings are combined, prioritized, and assigned, based on your assets, your exploit data, and your SLAs. Each fix goes to the team that owns it and is tracked until it’s closed, not just until a ticket is opened.
How it works
Findings come in from your scanners and cloud security tools.
Featured build
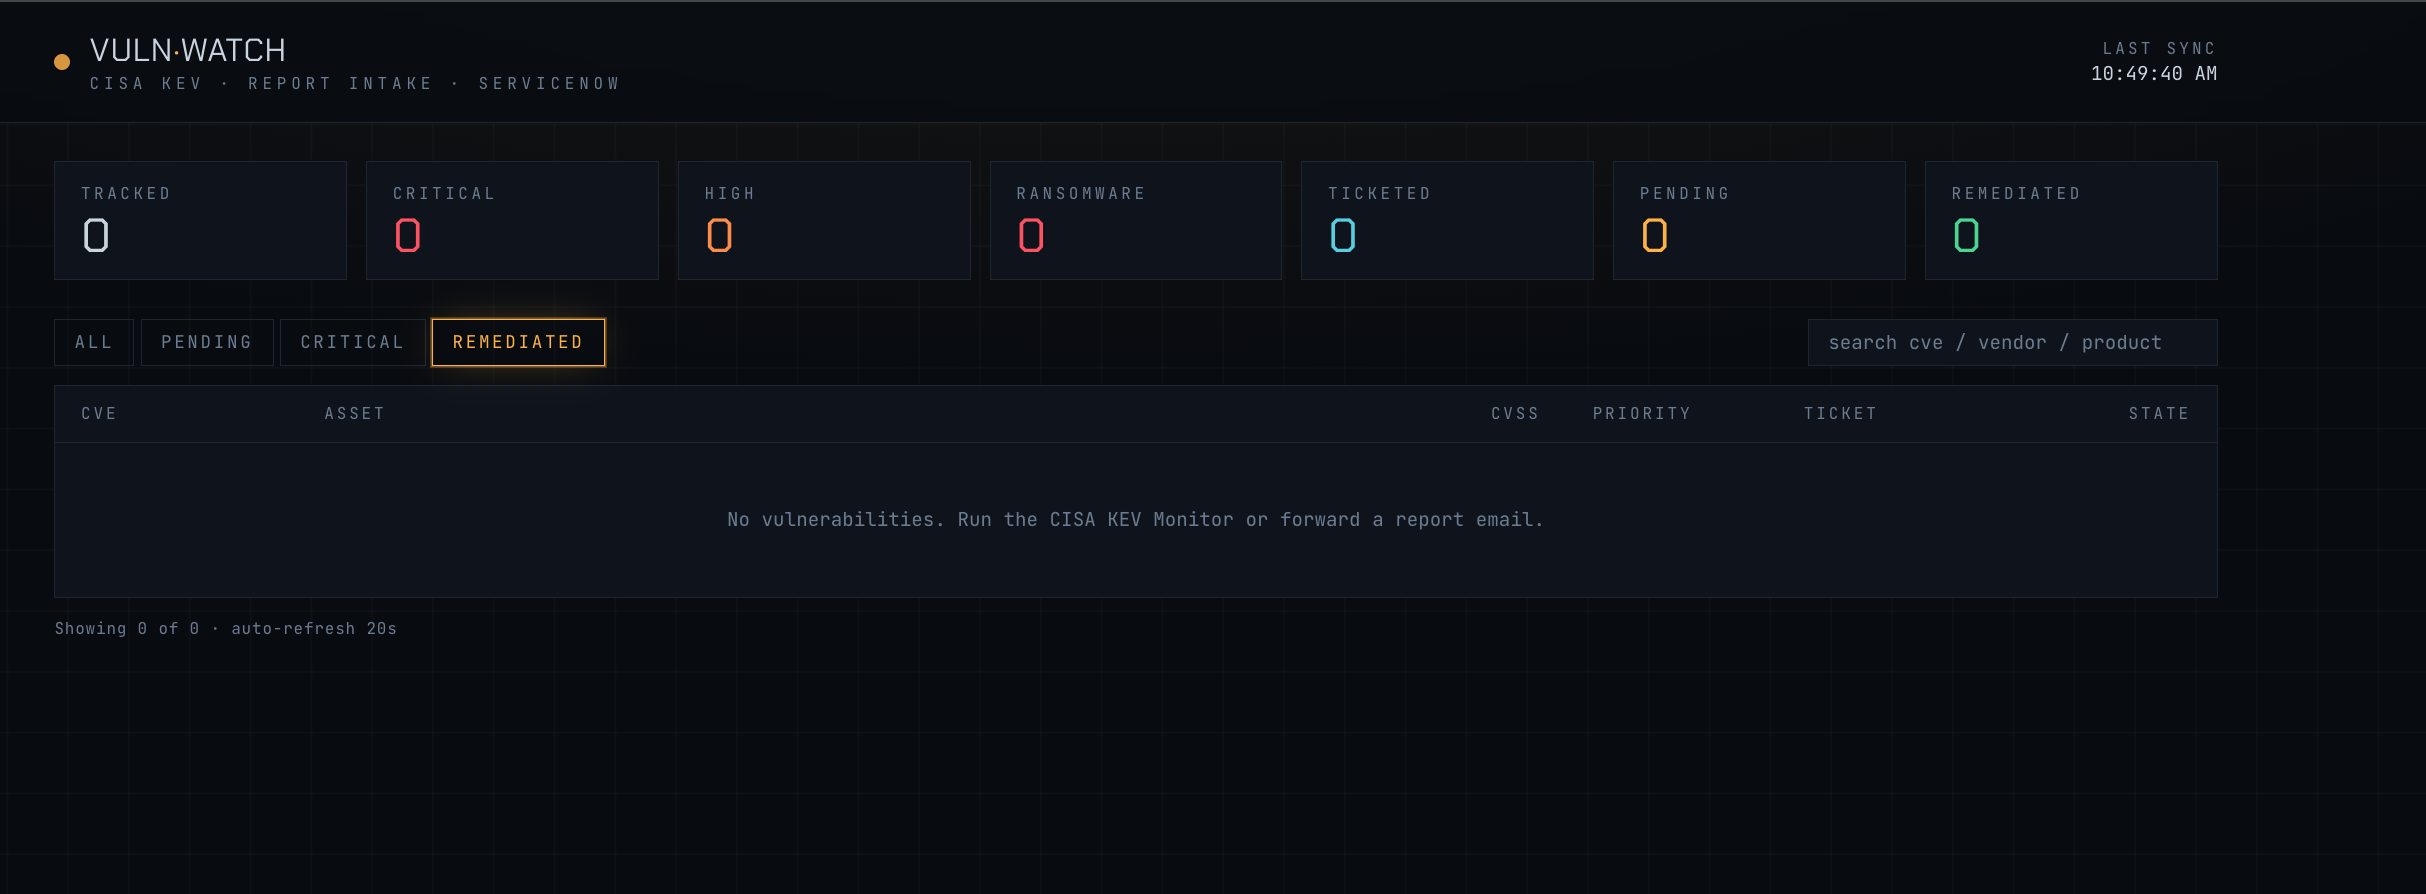
CISA vulnerability monitoring and ServiceNow ticket automation
This workflow monitors CISA's Known Exploited Vulnerabilities catalog and other sources for new CVEs, enriches each vulnerability with AI-generated severity assessments and remediation guidance, and automatically creates or updates ServiceNow tickets with the information security teams need to patch affected systems. An operator dashboard provides review and approval-gated remediation capabilities.
Examples
A gallery of real-world agents, apps, and automations, ready to use. Start from an example or a prompt, and shape it around how your team works.

 IT & SecuritySync CrowdStrike Spotlight vulnerabilities to Jira and auto-patch

 SecurityMatch new CISA vulnerabilities to your assets in Tenable
 SecurityTriage CISA KEV vulnerabilities from Slack with interactive buttons
- Security & ITThreat and vulnerability intelligence hub

 SecurityMonitor vendor security advisories for new vulnerabilities
Related use cases
 AI SOCTriage, enrichment, and escalation, with agents tuned to how your team works.
 SOAREnrichment, containment, and remediation, with each step running as you designed it.
 Threat intelligenceFeeds, indicators, and enrichment, with what matters routed to the right tools.
 Network securityFirewall rules, DNS, and proxies, with threats blocked across vendors.
 GRCEvidence, control testing, and vendor risk, with audits ready when you are.