
Your SOC has its own way of investigating, escalating, and closing alerts. But most AI SOC products only handle what their vendor planned for.
With Tines 3B, you start with pre-built triage agents and shape them around your detections, runbooks, and escalation paths. You decide what agents can resolve on their own, and when your rules call for a human, the investigation is already underway.
How it works
Connect your tools
Alerts come in from your SIEM, EDR, email security, and other tools.
Featured build
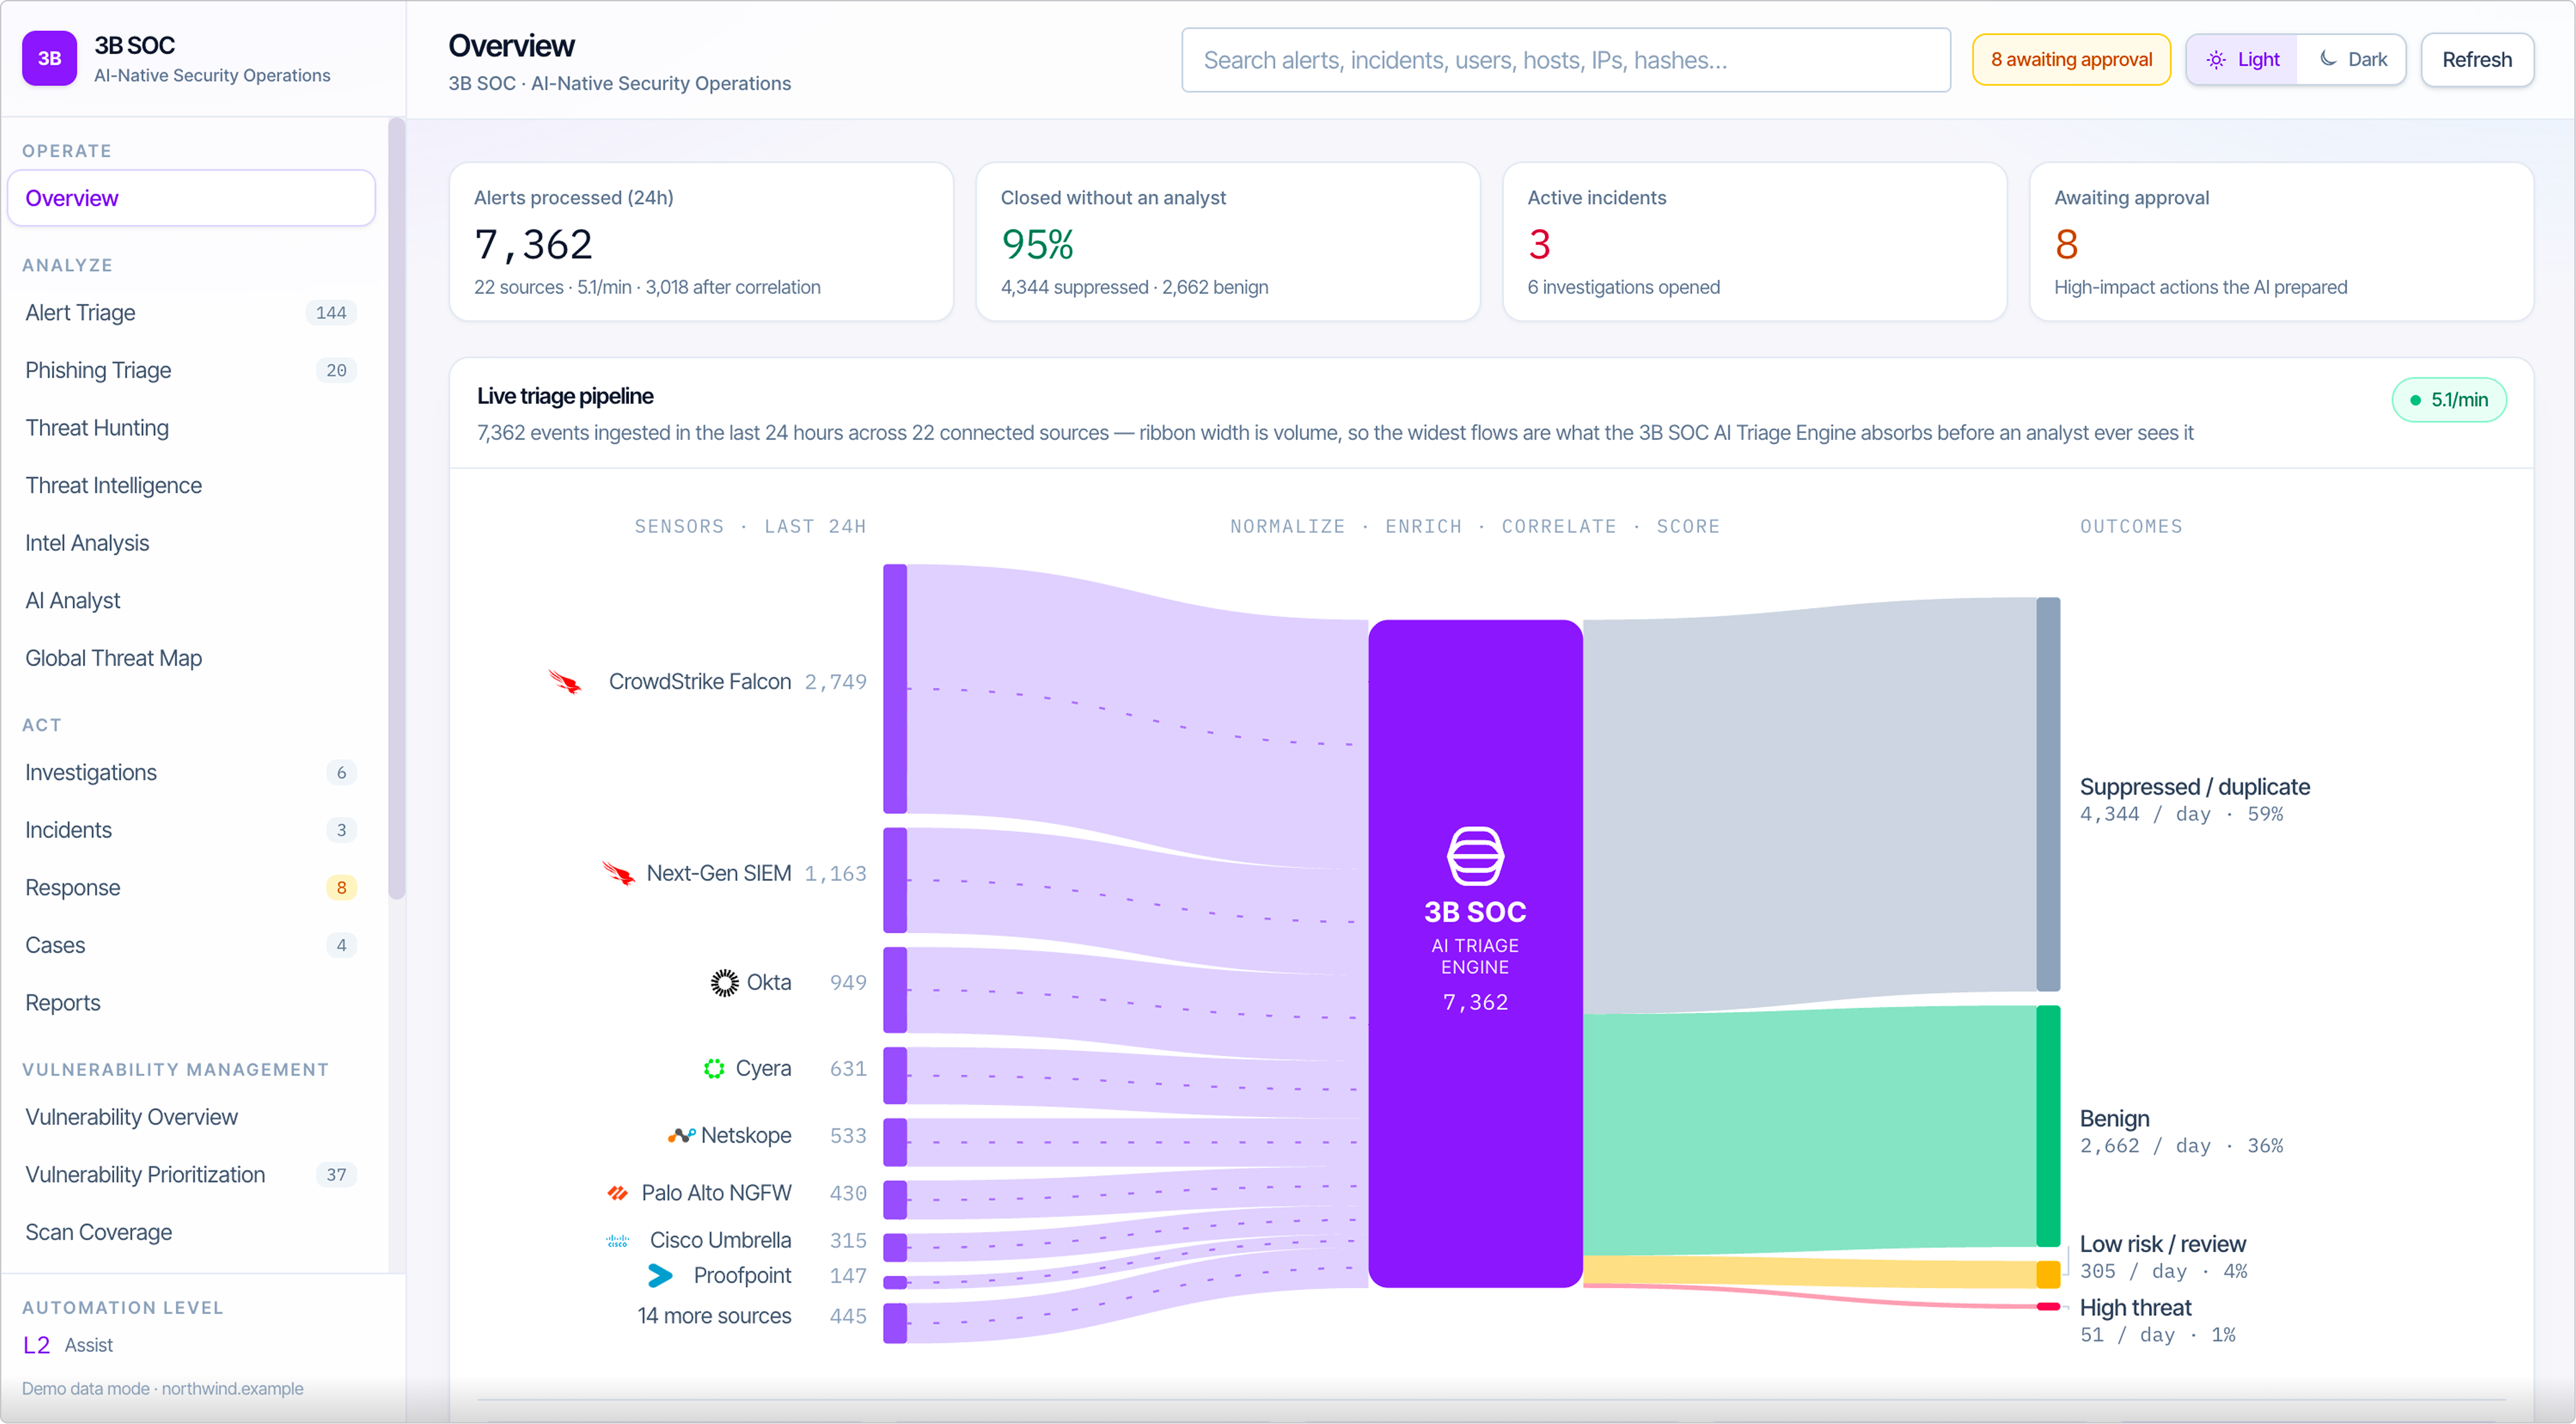
AI-native security operations center with governed incident response
This workflow is a comprehensive, AI-native Security Operations Center (SOC) demonstration environment that unifies alert triage, investigation, correlation, threat hunting, and incident response into a single command center. It operates on the principle that AI reasons, deterministic workflows execute, and humans approve high-impact actions, all within a strictly governed, auditable framework. The system addresses alert fatigue and tool fragmentation by normalizing telemetry from 22+ simulated security tools, automatically suppressing noise, correlating threats into visual attack chains, and enforcing approval workflows for containment actions.
Examples
A gallery of real-world agents, apps, and automations, ready to use. Start from an example or a prompt, and shape it around how your team works.
- Pre-built
 IT & SecurityAgentic threat hunting


 +7Security & ITAgentic alert triage driven by Confluence SOPs

 Security & ITAI-driven CrowdStrike alert triage, case creation, and response
 SecurityAgentic security alert response across EDR tools
- Security & ITSelf-calibrating SOC quality assurance with AI scoring and SOP improvement
Related use cases
 SOAREnrichment, containment, and remediation, with each step running as you designed it.
 Threat intelligenceFeeds, indicators, and enrichment, with what matters routed to the right tools.
 Vulnerability managementFindings, owners, and fixes, with the riskiest issues addressed first.
 Network securityFirewall rules, DNS, and proxies, with threats blocked across vendors.
 GRCEvidence, control testing, and vendor risk, with audits ready when you are.