Cases

Case management built around how your security team works

Security team / Cases /
Critical alert, host: MARTIN-PC (#36297)
Created 2d ago by Cases bot • 0 comments
D
In progress
Description
  • Case metrics
  • Runbook
Detection records
Initial detection and triage
Incident notification and coordination
Containment and isolation
Response and mitigation
Eradication and recovery
Followup records
Post-incident activities
Closure note
High
Critical alert, host: MARTIN-PC
Alert Incident
Case metrics
TypeCase timeSLA timeMet SLA?
TTDTo be updated with TTD time60 minTo be updated with TTD SLA result
TTRTo be updated with TTR time4 hrTo be updated with TTR SLA result

CrowdStrike detection received: View details below for further detection, behavior, and IP enrichment information.

Runbook

Go to Runbook

Initial detection and triage
CrowdStrike Falcon alerts about a potential security incident
Confirm the severity and priority level
Gather basic information about the alert, including affected hosts, observed behaviors, and timestamps
Verify if the alert aligns with known threat intelligence or attack patterns
Incident notification and coordination
Notify stakeholders, including the incident response team, SOC, and relevant IT personnel
Establish clear lines of communication and assign roles to team members
Create and incident ticket or record in your incident management system
Containment and isolation
Identify affected hosts and isolate them from the network to prevent further compromise
Engage CrowdStrike’s containment capabilities, if available, to isolate the affected hosts
Consider applying network-based controls to block associated suspicious traffic
Leverage CrowdStrike’s threat intel and community forums to gather additional info
Response and mitigation
Based on the findings, develop a mitigation plan to address the incident effectively
Apply necessary patches, updates or configurations to address any vulnerabilities found
Identify compromised user accounts, credentials, or access rights, and revoke or reset them as appropriate
Implement necessary changes to security policies, configurations, or access controls to prevent future similar incidents.
Cases bot created case #36297
4:32 PM
Cases bot added tags
4:32 PM
Alert Incident
Cases bot set priority to High
4:32 PM
Cases bot assigned
D
Darren
4:32 PM
Cases bot completed
4:32 PM
CrowdStrike Falcon alerts about a potential security incident
Add a comment...
Send

Bring investigations, response actions, and the people involved into one platform. Use Tines 3B to build workflows that keep cases up to date and help your team act on what they find.

Records

Capture data across workflows to report on this in a consistent, structured format.

Security teamStoriesCasesDashboardsRecordsSecurity alertsAlert IDTypeSeverityEmailA-17732Suspicious file transferHighjason@company.comA-17731Multiple failed login attemptsMediummryan@company.comA-17730Privilege escalHighdkim@company.comA-17729Data exfiltration attemptHighrobrien@company.comA-17728Phishing email reportedLowaphillips@company.comA-17727Unusual admin activityMediumtnguyen@company.comA-17726Malware detected on endpointHighlchen@company.comA-17725Impossible travel sign-inMediumsgarcia@company.comA-17724Suspicious OAuth grantMediummpatel@company.comA-17723Brute-force attempt on VPNHighewilson@company.comA-17722Phishing email reportedLowjlee@company.comA-17721Data exfiltration attemptHighkbrown@company.comA-17720Unusual API key usageMediumrmartin@company.comA-17719Ransomware behavior detectedHighcnovak@company.comA-17718New device sign-inLowahughes@company.comA-17717Disabled MFA on accountMediumpkhan@company.comA-17716Suspicious PowerShell commandHighjortiz@company.comA-17715Public link to sensitive fileMediumlfoster@company.com

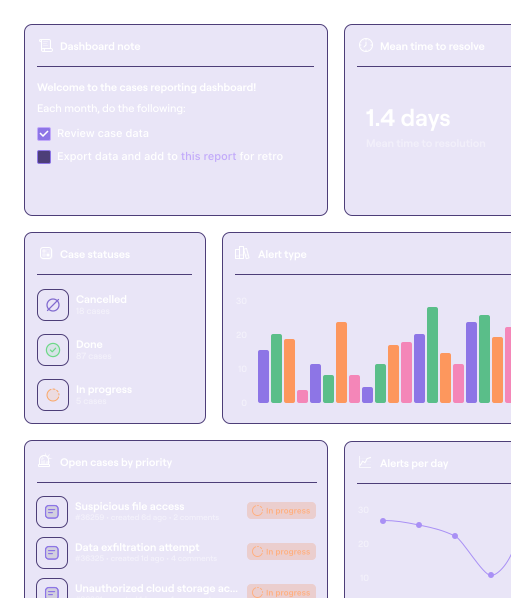
Dashboards

Monitor and report on workflow performance with cases and records in one location.
Case structures that fit your processes

Give incident response and vulnerability investigations the fields and templates each needs. Describe your requirements in Tines 3B to generate a structured case template, then refine it for your team. Tines 3B can update case details as new evidence arrives.

Bring every team involved into the investigation

Easily collaborate with IT, legal, and HR in the same case, with structures that support each team’s process. Use Tines 3B to build custom interfaces for the people contributing. Keep findings and decisions together, with less context lost across email and Slack.

AI + Cases

Put AI to work at the level you choose

Examples

  • Create and enrich cases from incoming alerts
  • Triage cases and route them to the right team
  • Summarize evidence and build investigation timelines
  • Draft reports for analyst review
  • Resolve cases where your team has chosen to automate resolution
Why Tines Cases?

Customizable

Build case templates around your processes. Generate a starting point with natural language in Tines 3B, then adapt the structure as things change.

AI-assisted

Let AI handle summarization and documentation, or give agents a role in triage and resolution. Set the level of autonomy for each case.

Connected

Create and update cases through Tines 3B and let analysts trigger agents or automations from within a case to act on their findings.

Collaborative

Give security and teams across your organization a shared place to investigate. Keep contributions and decisions in the case so the next person has the context they need.

Start building today

Cases can be added-on to Tines 3B or Tines Stories. Talk to one of our experts to learn more.

Talk to an expert

Sign up today to get started or schedule time with our team to learn more.