
Controls are tested once a year and assumed to work the rest of the time. When something drifts, it often shows up in an audit finding rather than when it happened.
With Tines 3B, you build monitoring the way your controls need it, whether that’s checks that run against live systems, a dashboard of control health across frameworks, or alerts to owners when something fails. You decide what’s tested, how often, and what counts as a failure. Each result is recorded with its evidence, so you know where you stand before the auditor asks.
How it works
Controls are mapped to your frameworks and the systems they depend on.
Featured build
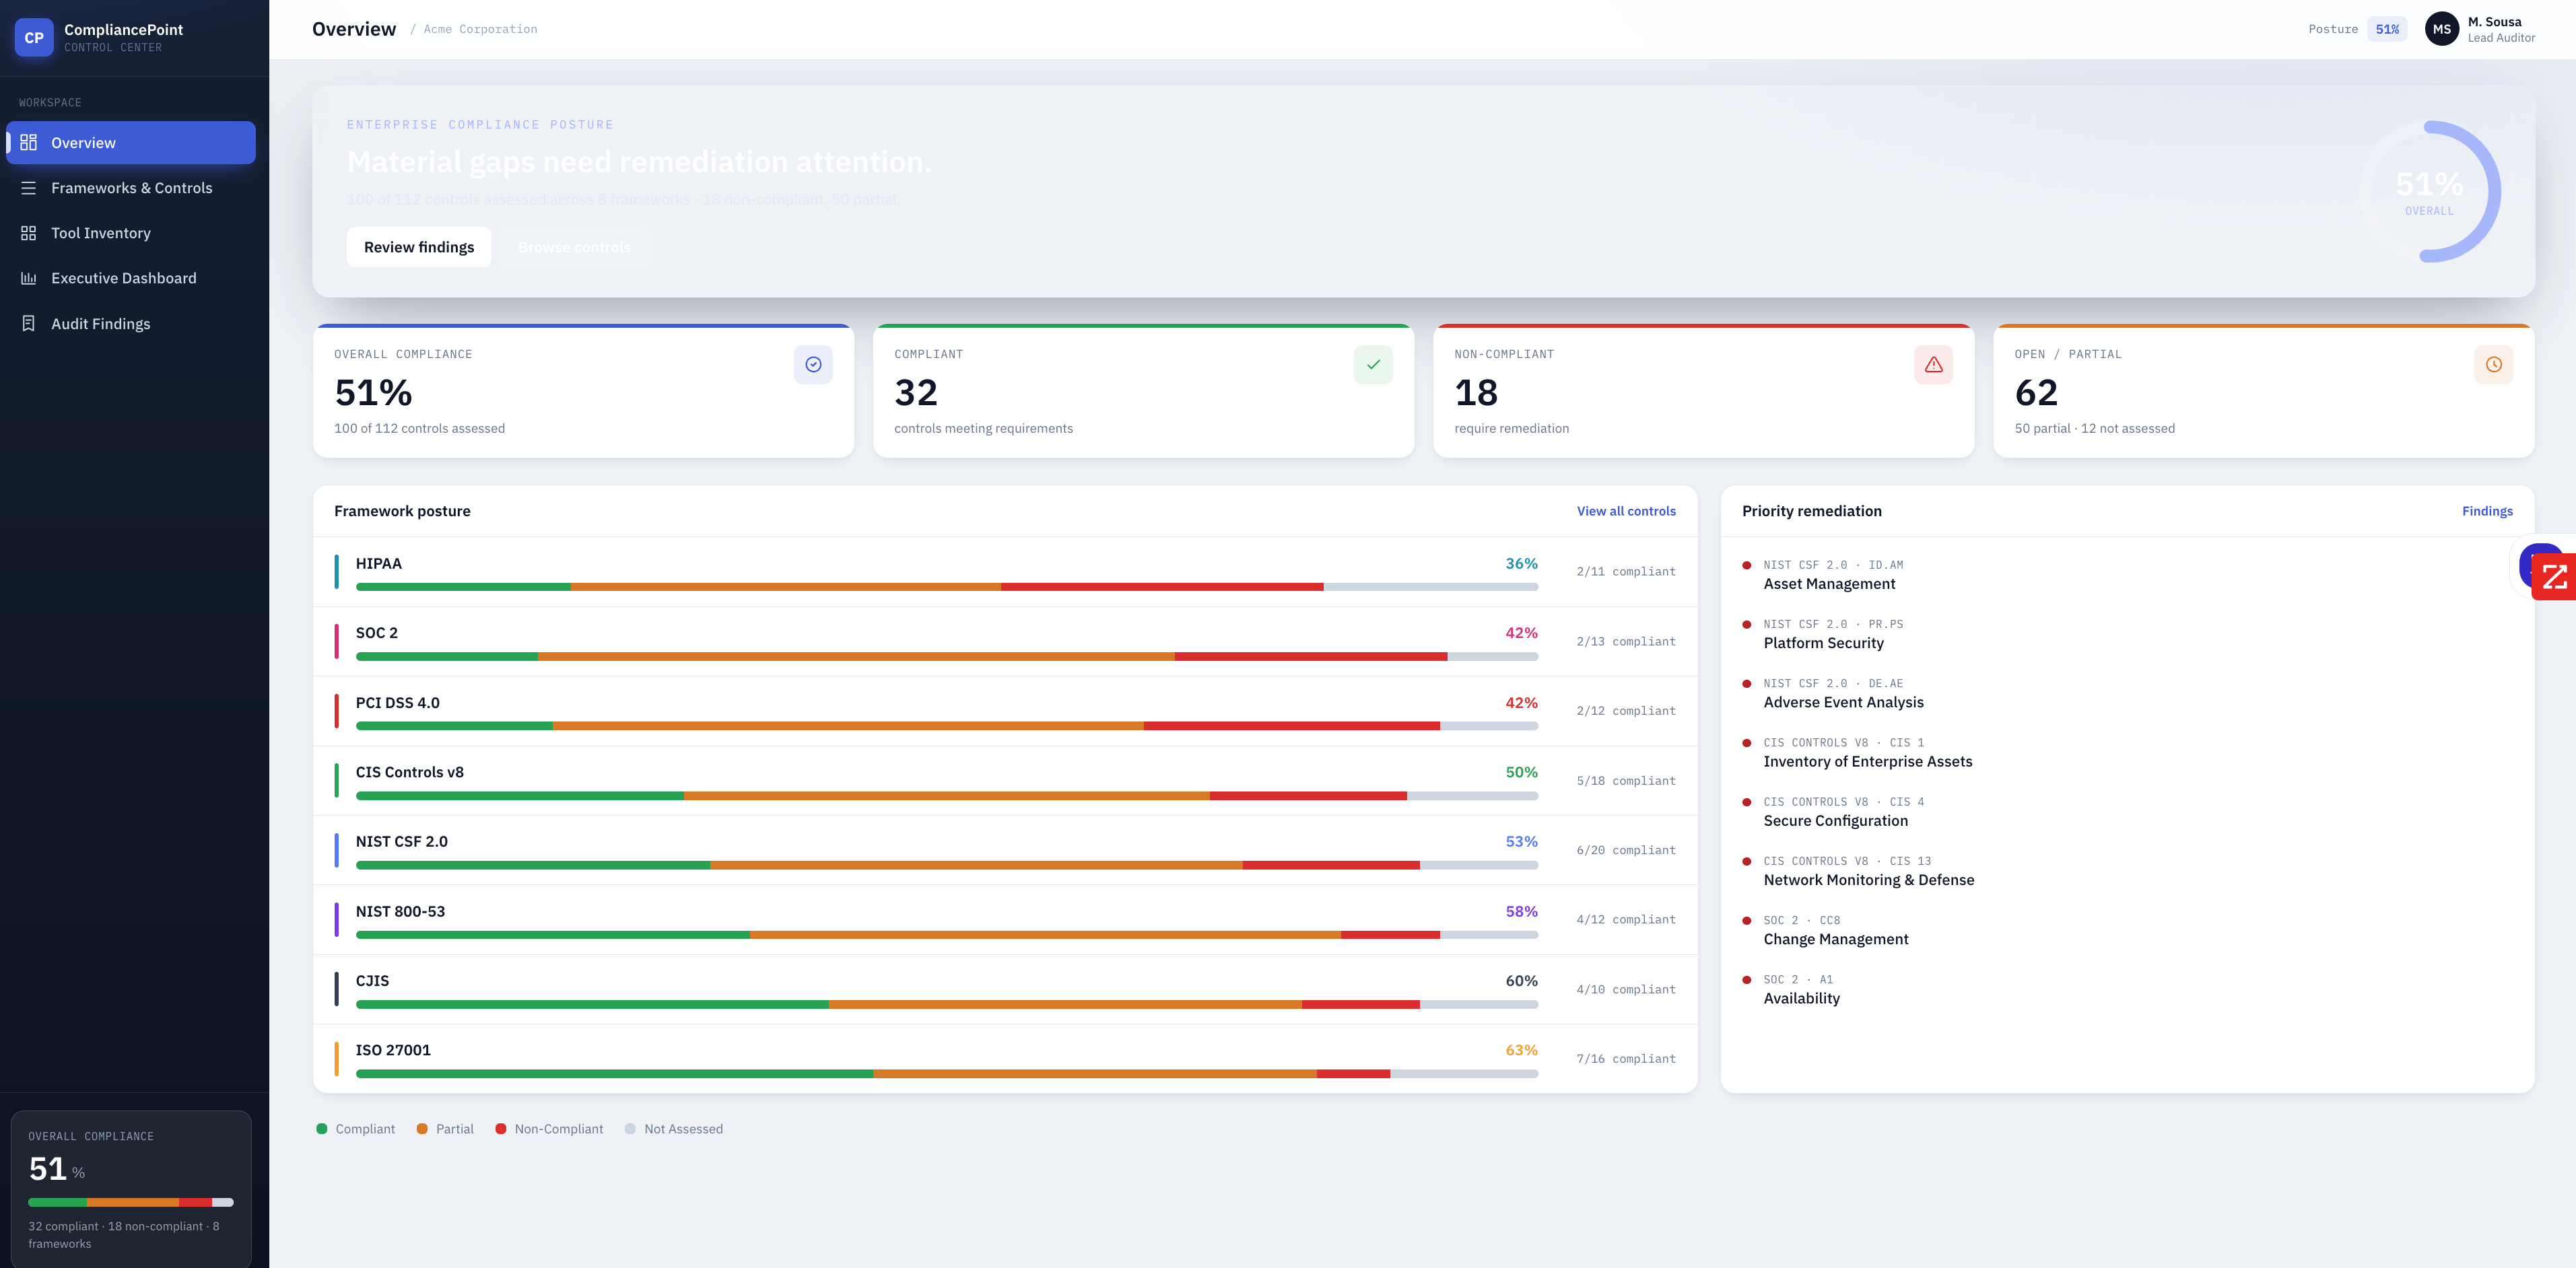
Compliance framework monitoring dashboard for GRC teams
A GRC web application that tracks an organization's compliance posture across eight major security and privacy frameworks (NIST CSF, CIS Controls, SOC 2, ISO 27001, PCI DSS, HIPAA, NIST 800-53, and CJIS). Auditors assess controls against the organization's security tool stack, record remediation plans, and generate executive scorecards. The system correlates tool coverage with control requirements to surface gaps and prioritize remediation efforts.
Examples
A gallery of real-world agents, apps, and automations, ready to use. Start from an example or a prompt, and shape it around how your team works.
- Pre-built
 IT, Security & HRAutomate macOS endpoint compliance checks with SimpleMDM
- Security, IT & FinanceCompliance control status board for SOC2, PCI-DSS, and GDPR


 +2Security & ITCJIS compliance monitoring tool
 Security & ITAutomated AWS security & compliance audit to Google Sheets
- SecurityAI-scored risk register for security and compliance teams
Related use cases
 Contract review and approvalTake the back and forth out of contract reviews.
 Legal intake and matter managementRequests arrive in one place, get triaged by type and risk, and land with the right member of the team.
 NDA generation and executionStandard NDAs drafted from your templates, sent for signature, and filed without a lawyer touching them.
 Data privacy and DSAR fulfillmentVerify the requester, find their data across systems, and respond before the statutory deadline.
 Regulatory reporting and compliance evidenceReports assembled from live system data, with the evidence behind them ready when regulators ask.
 Policy management and attestationPublish policies, collect acknowledgments, and follow up with anyone who hasn’t signed.
 Third-party contract and obligation trackingRenewals, notice periods, and commitments tracked across your contracts, so nothing lapses unnoticed.